B.Sc. Informatik · Einstieg im IT-Support · Windows Server & Active Directory
What I’m working on
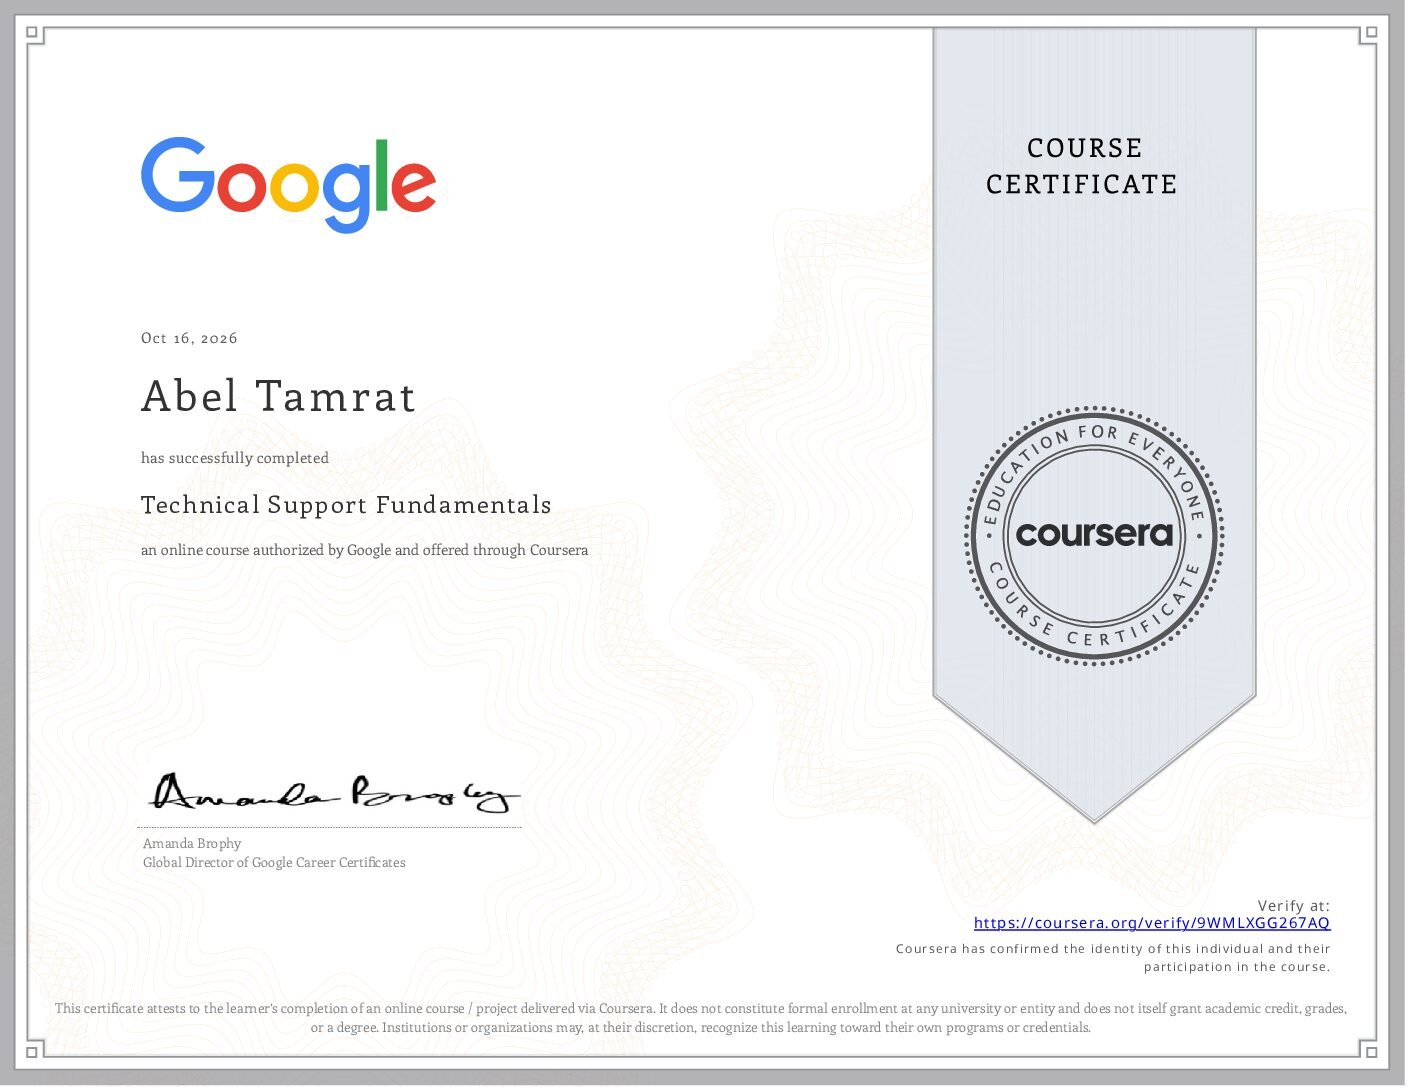
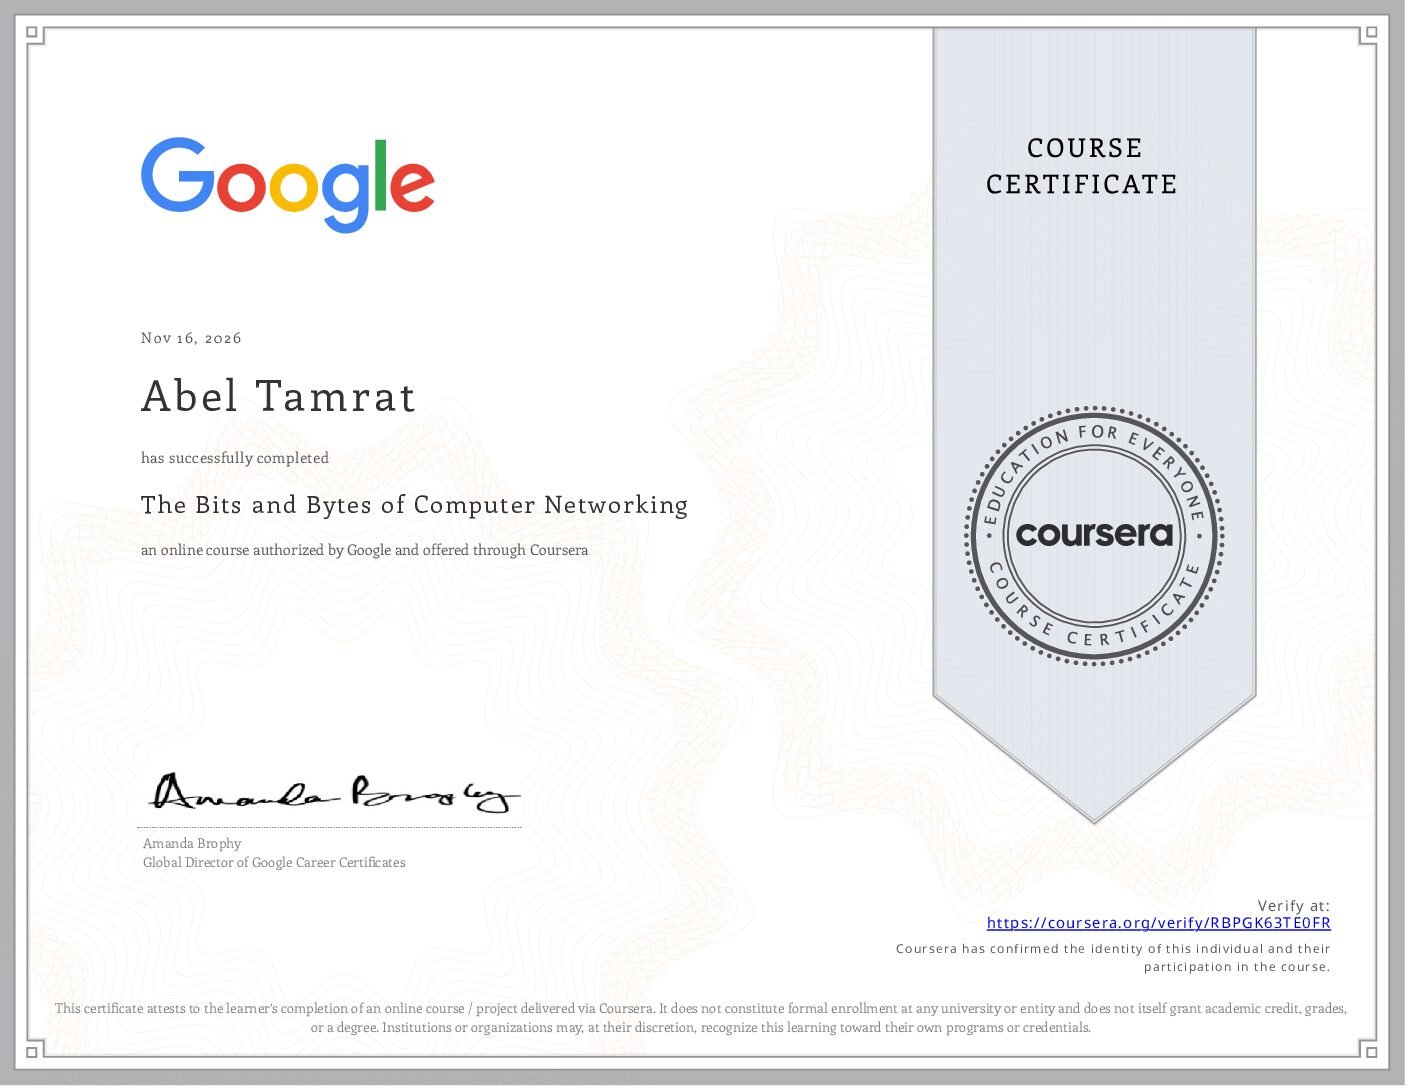
Google IT Support Professionals Certificate
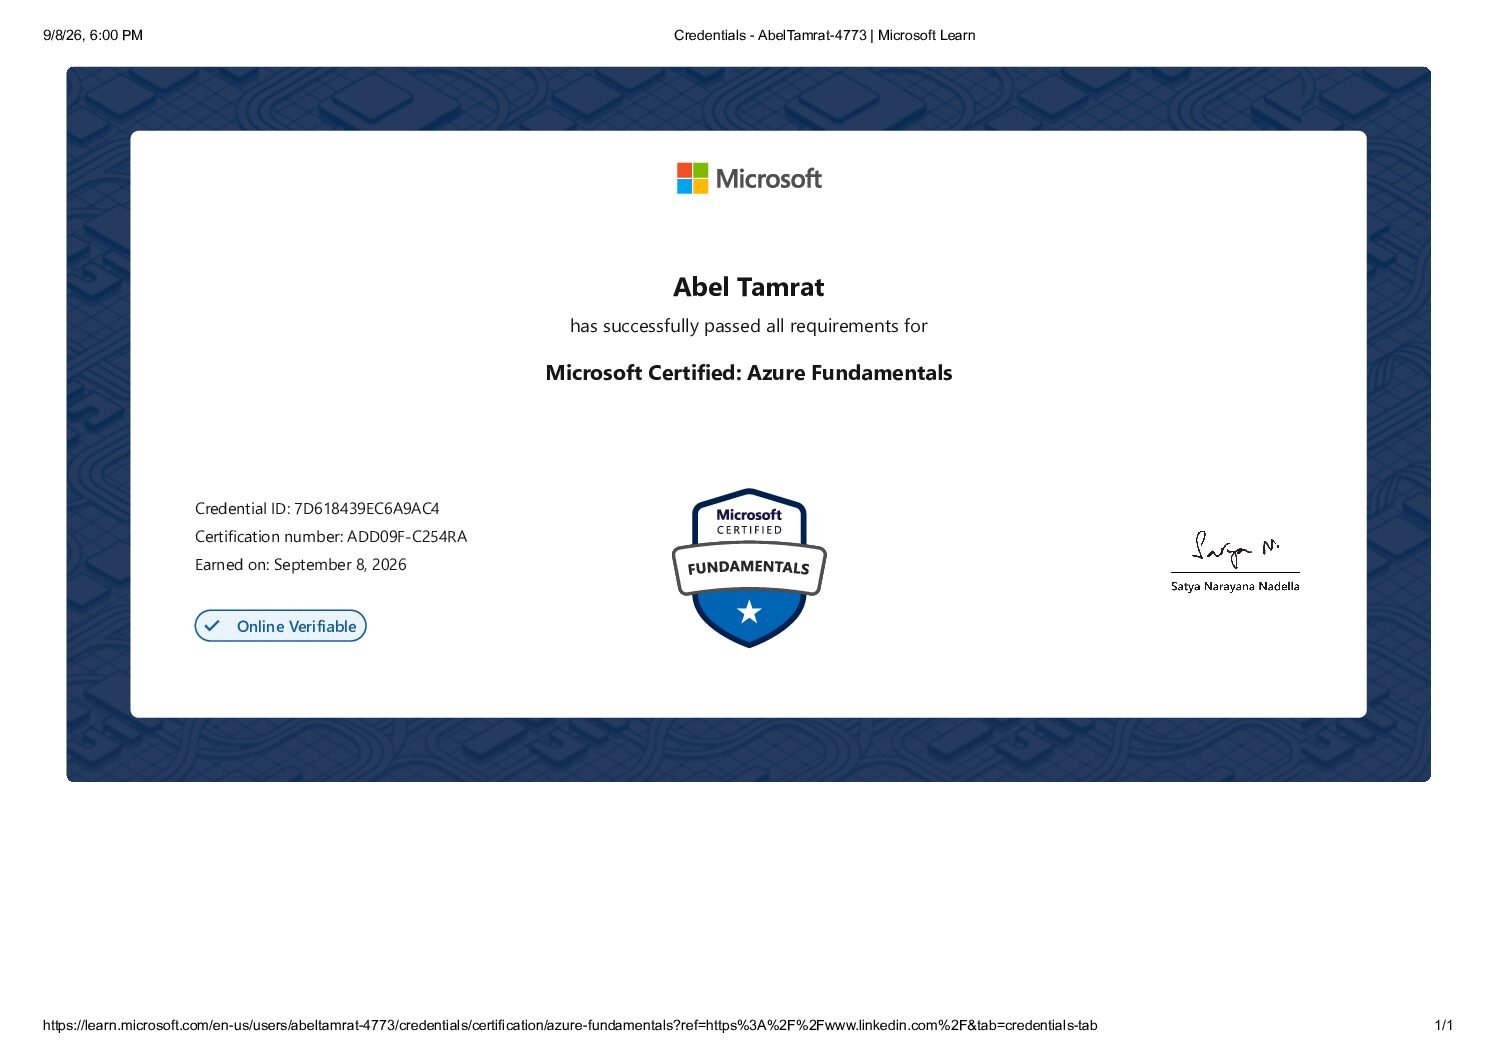
Already attained (2/6) certs
Projects
Sentinel Detection Lab
Ein Detection Lab auf Basis von Microsoft Sentinel, das den Arbeitsalltag eines SOC Analysten (Tier 1) abbildet. Eine Windows-Server-VM sendet Security Events und Sysmon-Daten per Azure Arc nach Sentinel. Mit Atomic Red Team habe ich vier Techniken aus dem MITRE-ATT&CK-Framework simuliert (T1136.001, T1053.005, T1547.001, T1087.001), mit KQL gesucht und als...
Active Directory Lab
Created a Windows Server VM in Azure resource group name: ad-lab-rg VM name: DC01 region: Germany West Central admin username: itscrxzabel static private IP: 172.16.0.4 Installed Active Directory Domain Services AD DS AD DS role showing installed in Server Manager No domain created yet 'Promote this server to a domain...
Experience
Active Directory Lab
Jake's Tech Lab, IT SupportNeufahrn bei Freising | November, 2026 - November, 2026
Built a complete Active Directory environment in Azure to practise common IT support and system administration tasks hands-on, from domain setup to user and permission management.
Skills: Active Directory · Windows Server · Microsoft Azure · User & Group Management · Group Policy · DNS · PowerShell · RDP · Network Security Groups
Projects Related
Sentinentel Lab
Homelab, SOC AnalystNeufahrn bei Freising | October, 2026 - November, 2026
Built a detection lab with Microsoft Sentinel to practise Tier 1 SOC work hands-on, from collecting Windows and Sysmon logs and simulating MITRE ATT&CK techniques to writing KQL analytics rules and triaging the resulting incidents. Skills: Microsoft Sentinel · KQL · MITRE ATT&CK · Windows Server · Azure Arc · Sysmon · Windows Event Logs · Security Operations (SOC) · Threat Detection